Showing posts with label Website Hacking. Show all posts

THE MOLE | AUTOMATIC SQL INJECTION TOOL | SQLI EXPLOITATION

 
The Mole - is an automatic SQL Injection exploitation tool. Only by providing a vulnerable URL and a valid string on the screwed up site, it can detect the type of  injection and exploit it, either by using the union technique or a boolean query based technique.
 
Features
  • Command line interface. Different commands trigger different actions.
  • Support for injections using Mysql, SQL Server, Postgres and Oracle databases.
  • Support for query filters, in order to bypass certain IPS/IDS rules using generic filters, and the possibility of creating new ones easily.
  • Developed in python 3.
  • Auto-completion for commands, command arguments and database, table and columns names.
DOWNLOAD
Complete Tutorial : Click here
 
Read More | comments

LOIC (Low Orbit Ion Cannon) | DOS | DDOS TOOL

LOIC (Low Orbit Ion Cannon) - named after a fictional weapon in the Command & Conqurer series of video games, is an open source network stress testing application, written in C#. LOIC performs a denial-of-service (DoS) attack or when used by multiple individuals, a Ddos (Distributed Denial Of Service) on a target site by flooding the server with TCP , UDP  or HTTP packets with the intention of disrupting the service of a particular host. People have used LOIC to join voluntary botnets.

Note  that i shall NOT be held responsible for your actions undertaken with the help of this tool.

WARNING: This is a very deadly tool, so please read the this sites disclaimer before using it. And  DO NOT attack from your computer because once you are traced? Only hell knows you are on your own, use it wisely :P:P:P

DOWNLOAD LOIC
Mediafire Password: code7
Read More | comments

HACK WEBSITE USING DotNetNuke (DNN) | PORTAL HACKING


Portal Hacking (DNN) - Is a type of website hacking technique that uses google to search for DNN vulnerable or hackable site. This is done with the help of google dorks. That is why it is known that google is one of the cyber elements that make a hackers job easier.

How to hack using (DNN)

  • In the google search box, type the following dork;

:inurl:/tabid/36/language/en-US/Default.aspx

The above dork is simply used to search for a DNN vulnerable site. see the image below;


  • Now let say that we have found a vulnerable site like; (just an example)

www.site.com/Home/tabid/36/Lan...S/Default.aspx

 All you have to do is modify the vulnerable url by replacing;

/Home/tabid/36/Lan...S/Default.aspx

with this;

/Providers/HtmlEditorProviders/Fck/fcklinkgallery.aspx 

So that you will have something that looks like this;

www.site.com/Providers/HtmlEditorProviders/Fck/fcklinkgallery.aspx


  • Now enter the modified url in address bar and hit Enter! You will get the link gallary


  •  Now on the ''link type'' menu select ''File'' and then replace the url in your browser's address bar with the following script and hit Enter!
  javascript:__doPostBack('ctlURL$cmdUpload','')

An ''upload'' option should appear on the link gallary menu as shown bellow;

  •  Now Upload your shell c99,c100, r57 etc ...... and its game over!!!  
Shells are a malicious PHP files which you will need to upload to any website, and once you execute it you will get access to its server directly WITHOUT authenticating your self. With a help of a shell you can easily remove/edit/replace files,. in shot taking over the server as if you where the admin :P
    Read More | comments

    HOW TO HACK A WEBSITE BY SQL INJECTION USING HAVIJ | TUTORIAL

    You can download Havij here

    After downloading and installing Havij SQL tool,. you have to find an SQL vulnerable site. This can be done by the use of google dorks like
    • inurl:index.php?id=sql under''
    Read this tutorial on manual sql under   '' searching for the vulnerability ''   here ...

    but for an easy go, you can just use another automated program known as sql poison . you can download  here. The main aim of sql poison scanner is to help you find a vulnerable web page by performing an automated blind search onto a search engine like google. Havij will only hack a website through a specific webpage which you know is vulnerable to sql injection.

    -----------------------------------------------------------------------------------------------------------------

    Now lets say that you have found a vulnerable weblink url which looks like this one:
    • http://www.hackyourdad.com/hisoffice.php?id=282
    1. Open havij, then copy and paste the vulnerable weblink as shown in figure


    2. Now click in the "Analyze" button


    4. After u click Analize, wait for it to find it's vulernable, type of injection, if db server is mysql and it will find database name. Then after get it's database is name like xxxx_xxxx


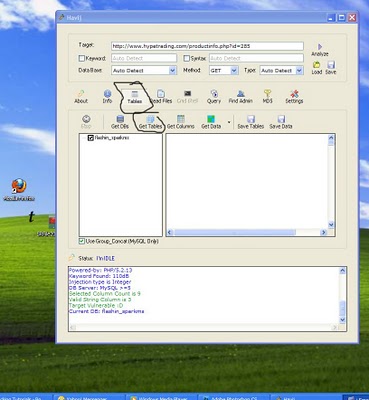
    5. Then go to the next operation of finding tables by clicking "tables" . A sub menu will appear  where you         will click "Get tables"  as shown in the figure below. Your may need to wait for a while before it shows         you the tables


    6. After you get the tables ,there will be a check box for "users" Put mark on it and click on the " get columns " tab as shown in figure


    7. Under ''Get columns'' list,.. just check on username and password and click on "Get data"

    8. Bingo!!! Now you have the Username and password that may be for the admin...The pass that you will get     will be in form of an md5 hash which you will have to decrypt it by using the MD5 decryptor tool as shown below

    After you have got the Username & the password ready,.. You now need to find the Admin page which will give you access to the control panel (cpanel) of the website.
    To find the Admin page, Go to ''Find Admin'' , then enter the site url on ''Path to search'' and click on ''Start'' as shown in the image below

    Now get the admin page url and open it in your internet browser,.. it will take you to a page which will request for the username and password,.. Enter these details & its Game Over!!! 
    You will find yourself in the control panel (cpanel) where you will have complete control of the website, you can do whatever the hell you want, you can even deface the website if you are realy in a bad mood :P

    Read More | comments

    HACKING EXTENSION FOR FIREFOX (XSS Me)


    Cross-Site Scripting (XSS) is a common flaw found in todays web applications. XSS flaws can cause serious damage to a web application. Detecting XSS vulnerabilities early in the development process will help protect a web application from unnecessary flaws. XSS-Me is the Exploit-Me tool used to test for reflected XSS vulnerabilities.


    DOWNLOAD
    Read More | comments

    Total Pageviews

    Free Automatic Backlink Free Auto Backlink
    japanese instant free backlink
    Free Automatic Backlink Service Malaysia Free Backlink ServicesFree Promotion LinkFree Smart Automatic BacklinkMAJLIS LINK: Do Follow BacklinkLink Portal Teks TVAutoBacklinkGratisjapanese instant free backlink Free Plugboard Link Banner Button

     
    Copyright © 2011. Ethical Hacking Unleashed . All Rights Reserved.
    Company Info | Contact Us | Privacy policy | Term of use | Widget | Advertise with Us | Site map
    Template modify by Creating Website